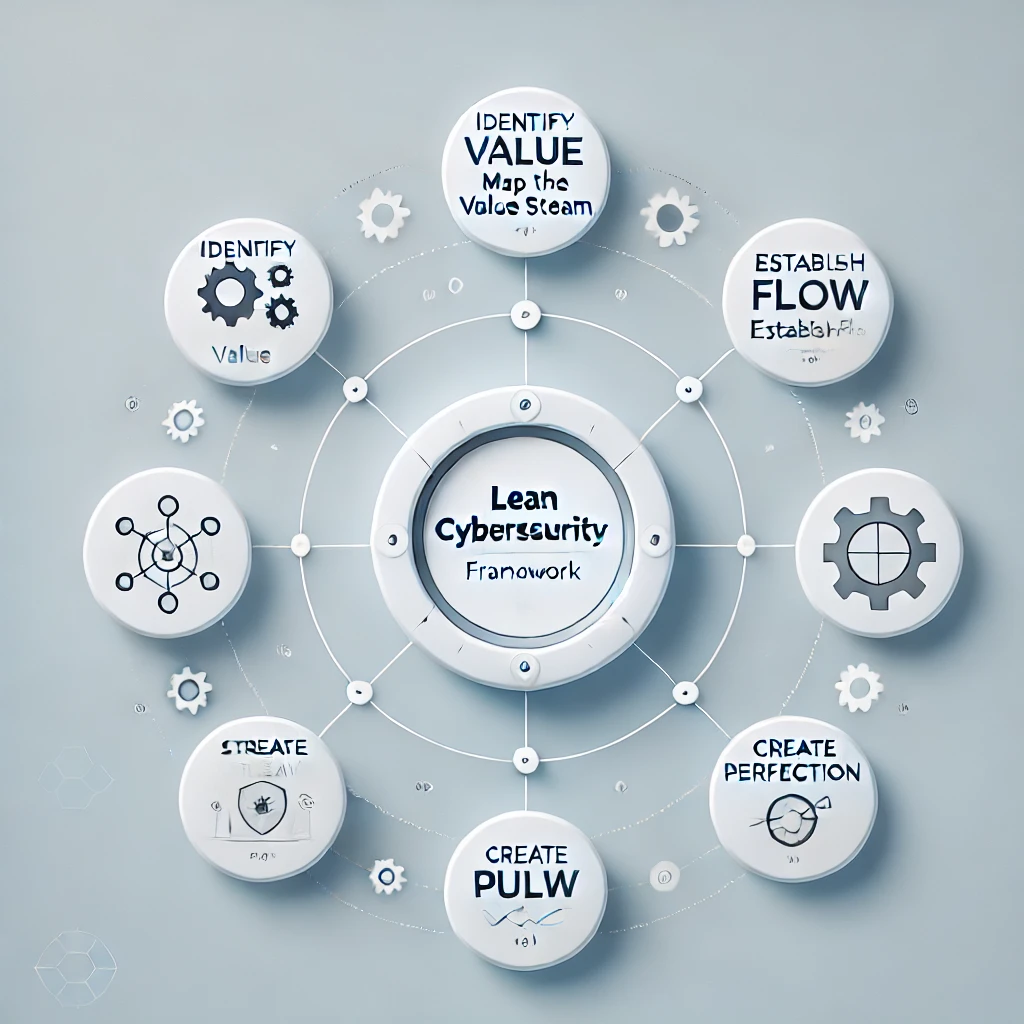
Cyberbrink’s Lean Cybersecurity Framework is our proprietary method for guiding organizations to streamline their cybersecurity operations, reduce complexity, and drive measurable results. By applying Lean principles to the core tenets of cybersecurity, Cyberbrink helps clients focus on delivering clear value, eliminating waste, and continually improving their security posture.
Cyberbrink Lean Cybersecurity Framework
1. Introduction
Cyberbrink’s Lean Cybersecurity Framework translates Lean thinking into cybersecurity best practices. This proprietary approach is designed to:
-
- Align security goals with business value
-
- Eliminate redundancy in processes and tools
-
- Develop a culture of continuous improvement
-
- Deliver measurable outcomes to demonstrate return on security investment
Through this framework, Cyberbrink partners with clients to design a cyber program that is optimized, efficient, and cost-effective, while ensuring that critical threats and vulnerabilities are addressed proactively.
2. Core Principles of Cyberbrink Lean Cybersecurity
2.1 Identify Value
-
- Business-Centric Security: Cyberbrink consultants work with stakeholders to align security controls with critical business functions, ensuring each control meaningfully protects vital assets.
-
- Risk-Based Prioritization: We focus on mitigating top risks that pose the greatest potential harm, avoiding scattershot security measures.
2.2 Map the Value Stream
-
- Tool & Process Inventory: Cyberbrink performs an in-depth review of the existing security stack to map each tool’s capabilities and usage.
-
- Identify Overlaps and Gaps: We pinpoint duplicate functionalities that can be removed or consolidated and highlight coverage gaps against high-impact threats.
2.3 Establish Flow
-
- Optimized Workflows: Cyberbrink helps design workflows that minimize bottlenecks, reduce manual handoffs, and enable faster response times.
-
- Automation & Orchestration: Where feasible, we introduce automation to reduce repetitive tasks and streamline operational efficiency.
2.4 Create Pull
-
- On-Demand Security Services: Security controls are provisioned exactly where and when needed, improving scalability and responsiveness.
-
- Tailored Threat Intelligence: We deliver relevant threat insights to the right teams at the right time, preventing “data overload” and wasted effort.
2.5 Pursue Perfection
-
- Continuous Improvement Cycle: Cyberbrink embeds Lean “kaizen” events to continually refine processes, measure performance, and implement incremental enhancements.
-
- Feedback Loops: Regular audits and reviews ensure the program remains relevant and effective amidst changing threats and business conditions.
3. Tools Duplication and Rationalization
3.1 Cyberbrink’s Technology Assessment
-
- Categorize Tools by Function: We classify each security solution—endpoint protection, SIEM, identity management, etc.—to visualize overall coverage.
-
- Redundancy Check: Tools offering similar or overlapping capabilities are flagged for consolidation or retirement.
3.2 Consolidate and Retire Redundant Solutions
-
- Vendor Negotiation & Consolidation: Cyberbrink leverages strategic partnerships to streamline licenses and minimize product sprawl.
-
- Integrated Ecosystems: Where appropriate, we suggest consolidated platforms that offer multiple, integrated capabilities rather than fragmented point solutions.
3.3 Cyberbrink Tool Governance Model
-
- Centralized Approval: A formal governance process ensures no new security technology is implemented without clearly defined objectives and ROI.
-
- Lifecycle Management: Periodic reviews validate whether existing tools remain fit for purpose or should be replaced.
4. Process Simplification
4.1 Mapping Critical Workflows
-
- Incident Response: Cyberbrink codifies standard procedures (from detection to root-cause analysis) to reduce meantime to contain (MTTC) and meantime to respond (MTTR).
-
- Vulnerability Management: We help unify scanning, triaging, patching, and reporting into a single, efficient workflow.
4.2 Cyberbrink Standard Operating Procedures (SOPs)
-
- Consistent Documentation: Concise, standardized SOPs outline key security processes, ensuring consistency across teams and shifts.
-
- Lean Governance: Approval points are minimal and meaningful to allow rapid decision-making without sacrificing control.
4.3 Agile Alignment
-
- Sprint-Based Enhancements: Incremental improvements to cybersecurity workflows are integrated into short, iterative sprints.
-
- Cross-Functional Collaboration: Security professionals embedded within operational teams foster a “security by design” mindset.
5. Efficiency and Productivity
5.1 Targeted Automation
-
- Security Orchestration, Automation, and Response (SOAR): Cyberbrink identifies high-volume, repetitive tasks (e.g., log analysis, threat enrichment) that can be automated.
-
- CI/CD Integration (DevSecOps): Automated code scanning and vulnerability checks early in development pipelines to catch issues before production.
5.2 Optimized Resource Allocation
-
- Role Specialization: Cyberbrink helps define role responsibilities, delegating high-complexity tasks to experts, and automating or outsourcing commodity functions.
-
- Training & Skills Development: Continuous upskilling ensures security teams fully leverage existing tools and stay current with emerging threats.
5.3 Metrics that Matter
-
- Detection & Response Times: Measure Mean Time to Detect (MTTD) and Mean Time to Respond (MTTR) for continuous performance evaluation.
-
- False Positive Reduction: Drive down alert noise to ensure security teams focus on genuine threats.
-
- Patch Lead Time: Track remediation speed for high-priority vulnerabilities.
6. Results-Driven Objectives
6.1 Key Performance Indicators (KPIs)
-
- Risk Posture Improvement: Cyberbrink defines risk-based KPIs that demonstrate quantifiable reductions in threat exposure.
-
- Cost Savings: We measure financial benefits from retiring unused or duplicative tools, reduced licensing fees, and improved staffing efficiency.
-
- Operational Efficiency: Track time saved through automated processes, simplified workflows, and integrated security efforts.
6.2 Governance and Reporting
-
- Executive Dashboards: Cyberbrink provides leadership with clear, concise updates on the overall security landscape, key metrics, and ROI.
-
- Regulatory Compliance: Our framework is adaptable to various standards (NIST, ISO, PCI-DSS); we streamline compliance with minimal overhead.
6.3 Continuous Feedback Loop
-
- Post-Incident Evaluations: Thorough reviews ensure lessons learned feed back into process improvements.
-
- Stakeholder Engagement: Regular surveys and communication keep all stakeholders involved in shaping the security strategy.
7. Cyberbrink’s Implementation Roadmap
-
- Phase 1: Assess and Plan
-
- Conduct a comprehensive cybersecurity maturity assessment
-
- Inventory existing tools and map current processes
-
- Establish baseline metrics (MTTD, MTTR, patch lead times)
-
- Phase 1: Assess and Plan
-
- Phase 2: Rationalize and Simplify
-
- Identify duplicate tools; consolidate or retire unneeded solutions
-
- Develop standardized, streamlined procedures for incident response, vulnerability management, etc.
-
- Phase 2: Rationalize and Simplify
-
- Phase 3: Automate and Integrate
-
- Implement SOAR and other automation techniques
-
- Integrate security within DevOps practices to “shift left”
-
- Phase 3: Automate and Integrate
-
- Phase 4: Measure and Refine
-
- Continuously track KPIs (risk reduction, cost savings, efficiency gains)
-
- Conduct regular Kaizen events to uncover and implement incremental improvements
-
- Phase 4: Measure and Refine
-
- Phase 5: Scale and Sustain
-
- Formalize ongoing governance, auditing, and training
-
- Evolve the security program as business needs and threats change
-
- Phase 5: Scale and Sustain
8. Conclusion
Cyberbrink’s Lean Cybersecurity Framework is our proprietary approach to helping organizations establish a robust, yet streamlined security posture. By systematically removing duplicative tools, simplifying processes, automating routine tasks, and measuring outcomes, we ensure that your cybersecurity investments are both efficient and effective.
Through continuous collaboration, iterative improvements, and a focus on tangible results, Cyberbrink empowers organizations to stay ahead of evolving threats while optimizing costs and resources. Our clients can confidently demonstrate to stakeholders that security initiatives are tightly aligned with business objectives—delivering real, measurable value.
Contact Cyberbrink
For more information on how Cyberbrink can help deploy our Lean Cybersecurity Framework in your environment, please contact us at:
Email: info@cyberbrink.com
Phone: +1 (201) 500 5688
We look forward to partnering with you to create a lean, resilient cybersecurity strategy.